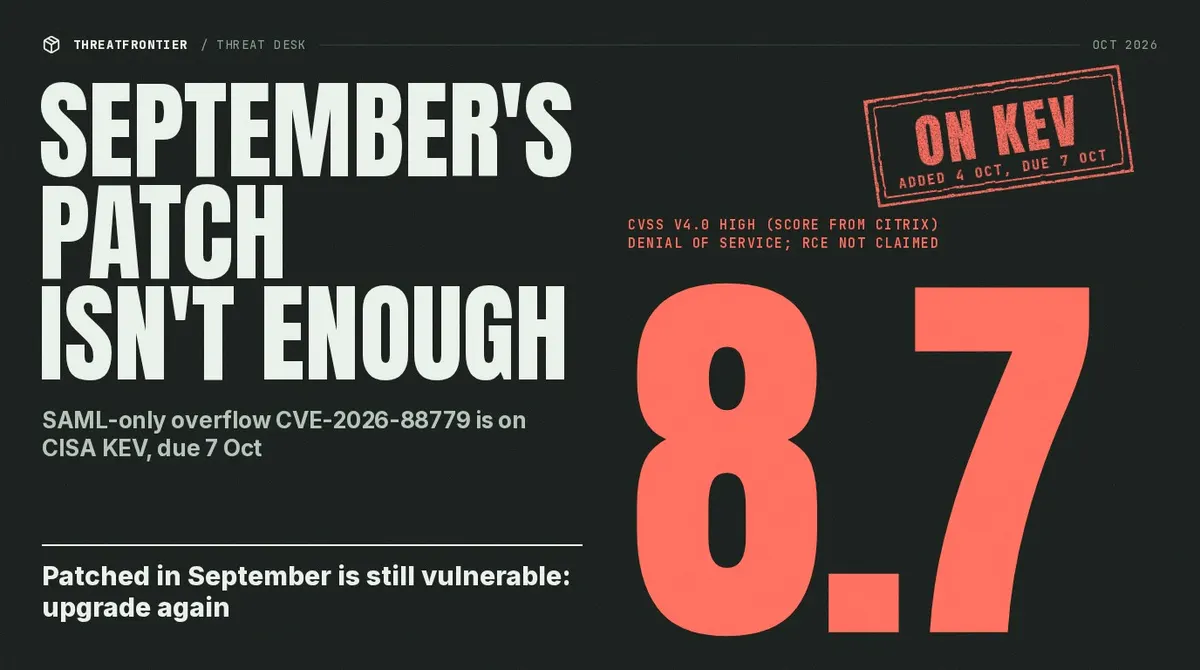
Tuesday, 7 October 2026 is the remediation due date for U.S. federal civilian agencies under CISA’s (Cybersecurity and Infrastructure Security Agency) KEV listing for CVE-2026-88779 in Citrix NetScaler ADC and NetScaler Gateway. The flaw — a memory buffer issue in SAML authentication (Security Assertion Markup Language, federated sign-in) when Gateway or AAA features are enabled — was added as actively exploited on 4 October. The KEV entry requires vendor mitigations aligned with BOD 26-04 risk-based patching and CISA’s forensic triage expectations for internet-exposed assets.
For Nordic and European organisations without a federal mandate, the date is still a sharp risk signal. When CISA sets a three-day deadline and marks “Forensic triage required per BOD 26-04,” it communicates confirmed exploitation and that patching alone may not be enough: log review, crash patterns, and follow-on intrusion indicators matter. Citrix has already shipped fixes (including 14.1-73.41 and 13.1-64.28) and describes denial-of-service (DoS) as the primary impact, while administrators and researchers continue to report suspected remote code execution via SAML surfaces.
Deadline day is a practical moment to ask three internal questions: Do we run SAML SP or IdP on NetScaler (`add authentication samlAction` / `add authentication samlIdPProfile`)? Are we on builds that actually address CVE-2026-88779, not only the earlier October patches for CVE-2026-88771–88778? Have we preserved artifacts — `nsaaad` crashes, Pitboss reboots, suspicious authentication requests — if we need to investigate pre-patch exploitation?
Many environments mirror the weekend pattern: recently patched appliances still crash when SAML is exercised, and vendor deny lists supplement but do not replace upgrade. The KEV note lists ransomware use as “Unknown,” which does not rule out actors using outages or potential code execution as a step toward later extortion or lateral movement.
What IT and security leads should do today
Inventory every NetScaler instance using SAML, compare build numbers against Citrix CTX697174, and install fixes immediately if you are behind. Treat internet-exposed, unmitigated appliances as potentially compromised until logs prove otherwise: preserve authentication, VPN, and system logs before rotation. Run triage under your DFIR process and CISA BOD 26-04 guidance where it applies to your sector. Brief leadership that U.S. KEV deadlines often trigger vendor and insurance scrutiny even for non-federal customers on the same product stack.
Evidence status
This deadline-focused brief rests on the CISA KEV record (added 2026-10-04, due 2026-10-07), Citrix advisory CTX697174, and public reporting on active exploitation and SAML preconditions; technical background was published by Forensix on 5 October.
A KEV deadline is also a communications problem. Security teams need to show that owners of identity and network platforms understand NetScaler often sits between users and core operations — not only as VPN but as a SAML bridge into cloud services. If patch windows slip, document the decision with risk acceptance, compensating controls (temporary unpublishing, tighter WAF rules, enhanced logging), and log-retention plans. CISA’s language about evaluating internet exposure per asset means an internally labelled “staff only” gateway that is still reachable via misconfigured split DNS may count as exposed.
The vendor has urged customers to verify SAML configuration before assuming September or early October updates are sufficient. That distinguishes this CVE from many “just patch” cases: the precondition is functional, not only a version string. In Nordic public-sector environments where SAML is standard for citizen and partner login, a wrong call can mean both an availability crisis and a confidentiality incident if attackers later prove code execution.
Finally, deadline day is not the end of exploitation. Actors who already established persistence or stole sessions do not vanish when the clock passes midnight in Washington. Plan continued monitoring of authentication failures, unexpected admin accounts, and outbound connections from NetScaler subnets after patching, in line with BOD 26-04’s emphasis on triage rather than a compliance checkbox alone.